AML Compliance Frameworks are Adapting to Complex Regulatory Environments
The move toward stronger group-level controls is creating more detailed expectations for how financial institutions manage compliance across different entities and jurisdictions. The new European framework is not limited to requiring a common AML policy. It also addresses information sharing, governance, risk assessment and the measures needed when local legal requirements differ from European standards.
This makes AML compliance frameworks increasingly dependent on clear responsibilities between parent undertakings, subsidiaries and branches. Group-level oversight can provide a consolidated view of money laundering and terrorist financing risks, while individual entities remain responsible for applying controls that reflect their own business activities and exposure.
Information Sharing is Becoming a Core Control
One of the most important developments concerns the movement of AML information within financial groups. Group-level policies are expected to support information sharing for AML/CFT purposes while maintaining appropriate safeguards around confidentiality and data protection. This creates a more structured relationship between individual compliance functions and the wider group.
The change is particularly relevant where risk information is distributed across multiple markets or business lines. A customer relationship, transaction pattern or geographic exposure identified by one entity may have implications elsewhere within the organisation. More consistent internal information flows can therefore help group compliance teams develop a broader assessment of risk rather than treating each entity as an isolated operation.
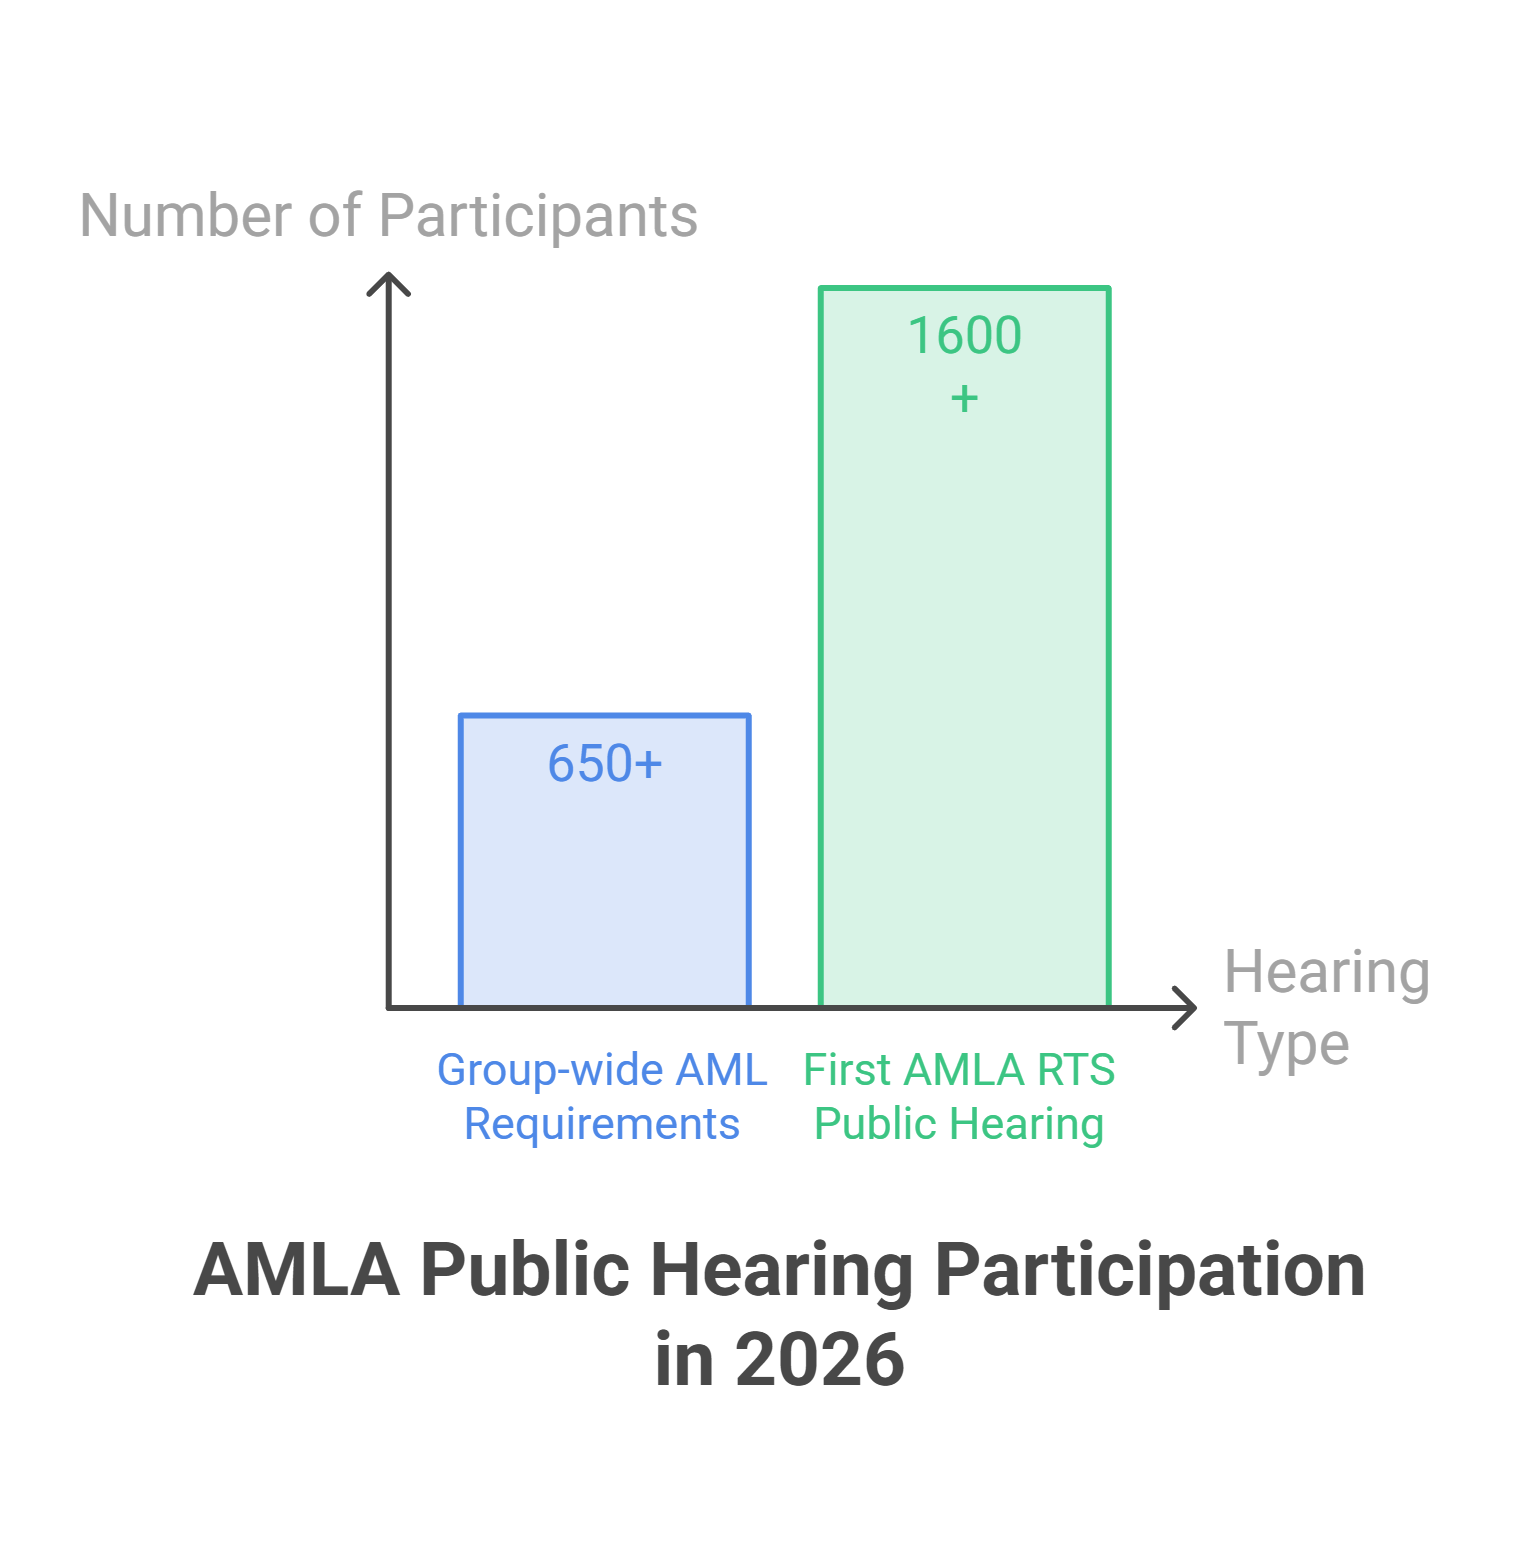
AMLA’s draft technical standards are intended to provide greater detail around these arrangements. The regulatory direction is toward common minimum requirements while recognising that subsidiaries and branches can face different operational and legal conditions. AML compliance frameworks therefore need to balance central oversight with appropriate local implementation.
Third-Country Operations Add Further Complexity
The challenge becomes more pronounced when financial groups operate in jurisdictions where local AML requirements differ from those applied within the European Union. Under the new framework, EU-based groups must take measures to ensure that third-country branches and subsidiaries remain subject to appropriate AML/CFT controls.
Where local legislation prevents the full application of EU requirements, additional measures may be needed to manage the resulting money laundering and terrorist financing risks. This means compliance teams need to assess not only whether a control exists, but whether it can operate effectively within the legal environment of the relevant jurisdiction.
The framework also strengthens group-level accountability. A group compliance manager is expected to oversee implementation of group policies and report to the management body of the parent undertaking, including on deficiencies requiring corrective action. This creates a clearer connection between operational compliance activity and senior-level governance.